
 2026
Archive · since 2022
Every talk
we've ever
recorded.
Free, like it should be. Browse 104 practitioner-led sessions on vehicle cyber security from every edition of Secure Our Streets. Filter by year, search by title or speaker, click any thumbnail to watch on YouTube.
2026
 2025
 2025
 2025
30 mins
 2025
60 mins
KEYNOTE | Product Cybersecurity in Practice Aligning Standards, Contracts, and Industry Needs
- Dr. Mathias Dehm Chief Product Security & Privacy Officer, AUMOVIO Germany
This presentation explores the evolution of product cybersecurity requirements in the automotive industry, highlighting the influence of emerging regulations such as UN ECE R.155 and standards like ISO/SAE 21434 on the cybersecurity landscape. It also addresses…
Slide deck 2025
33
Enhancing Automotive IDPS with CHERI based RISC Memory Protection for Improved Security
- Saket Mohan Founder and CEO, Secure Elements
- Sampath Kalutharage Cybersecurity and AI Lead Engineer, Secure Elements
The rapid integration of connected technologies in modern vehicles has introduced significant cybersecurity challenges, particularly in securing critical systems against advanced threats such as IP spoofing and rule manipulation. This study investigates the application of CHERI…
Slide deck 2025
39 Mins
Post Quantum Cryptography in Automotive A Strategy Proposal
Dennis Naujoks, Consultant for Automotive Security, ETAS Germany
Asymmetric cryptography is now in widespread use, but algorithms that are secure today will be broken by the quantum computers of tomorrow. Most of todays and upcoming automotive security measures (e. g. ECU integrity protection, secure…
Slide deck 2025
46 Mins
Automotive Ethernet Security Revisited New Protocols, New Attacks, and Advanced Scapy Techniques
- Dr. Nils Weiu00df CEO & Co-Founder, dissecto GmbH
- Jonas Horreis Senior Penetration Tester dissecto GmbH
Five years ago, we presented “Automotive Penetration Testing with Scapy” at TROOPERS19—a talk that quickly became one of the most-watched sessions on the TROOPERS YouTube channel. In the intervening years, the automotive domain has evolved significantly,…
Slide deck 2025
33 Mins
Automotive Threat Analysis and Risk Assessment Data sharing using openXSAM format
- Sergio Scabar Cybersecurity Manager, ZF Engineering Solutions
This study examines the automation of converting Threat Analysis and Risk Assessment (TARA) data into the openXSAM format within the automotive industry, addressing the growing need for cybersecurity in modern, interconnected vehicles. By leveraging both qualitative…
Slide deck 2025
46 Mins
Source vs Binary code analysis Challenges and Solutions within the Software Supply Chain
- Irina Kimmel Product Manager for Automotive Vulnerability Management, ETAS GmbH
This presentation explores the complexities and best practices in vulnerability management within the automotive software supply chain, with a focus on the challenges in complex software, including open-source components, third-party libraries, and proprietary software. The most…
Slide deck 2025
38 Mins
Under the Hood Tracking API Exploits Before They Hit the Road
- Elad Robb Director of Cyber Threat Intelligence, Upstream Security
- Ruslan Gurbanov Senior Cyber Security Solution Engineer, Upstream Security
APIs are the backbone of today’s connected vehicle ecosystem—powering everything from remote commands, over-the-air updates, to EV charging—but they’re also becoming prime targets for attackers. While cybersecurity teams focus on perimeter defenses and known vulnerabilities, API…
Slide deck 2025
42 Mins
Crypto Agility in Automotive Real Time Systems in Context of Post Quantum Cryptography
- Martin Manthe Lead Software Engineer Embedded Security, IAV
- Dr. Claude-Pascal Stoeber-Schmidt Technical Sales Manager u2013 Cluster SDV Enabler, IAV
- Philipp Jungklass Team Manager Embedded Security, IAV
Due to the recent advances in the development of powerful quantum computers, the issue of cryptographic agility has once again become a focus of cyber security. While increasing the key lengths of existing algorithms has primarily…
Slide deck 2025
45 Mins
Edge AI in Automotive Cybersecurity Challenges and Opportunities
- Gregor Knappik Senior Cybersecurity Solutions Architect, VicOne
- Krzysztof Skrzypek Senior Cybersecurity Engineer, VicOne
As vehicles evolve to be more software-defined, automotive cybersecurity must also adapt to meet the demands of increased system complexity, real-time threat detection, and distributed architecture. Edge AI, the deployment of artificial intelligence directly on a…
Slide deck 2025
44 Mins
ISO SAE 21434 based Automotive Risk Assessment Revisited
- Jean-Baptiste Mangu00e9 Embedded Architecture & Connectivity Cybersecurity Expert, AMPERE - AMS-AAC
Threat Analysis and Risk Assessment (TARA) is one of the cornerstones for complying with UN-R155 automotive cybersecurity regulation. In fact, the UN-R155 requires OEMs to perform risks assessments and demonstrate the appropriate management of risks throughout…
Slide deck 2025
45 Mins
PIBuster Exploiting a Common Misconfiguration in CCS EV Chargers
Marcell Szakály, DPhil Student in the Systems Security Lab, University of Oxford
This paper presents PIBuster, a new attack vector against the EV charging infrastructure. The attack targets the Qualcomm HomePlug GreenPHY modems used inside CCS chargers and vehicles, and is enabled by a common misconfiguration in their…
Slide deck 2025
40 Mins
Enhancing UN R155 to Address AI Specific Cybersecurity Risks
- Natasha Alkhatib Cybersecurity Leader, Symbio
This presentation explores the integration of Artificial Intelligence (AI), particularly Large Language Models (LLMs), in safety-critical automotive systems and the emerging cybersecurity risks they introduce. We discuss the current gaps in regulations like UN Regulation No.…
Slide deck 2025
43 Mins
Exploit Story Reverse Shells on the Road Hacking Vehicle Infotainment
- Abhay Vishnoi Security Researcher, KPIT
This session explores how modern vehicle infotainment systems can be exploited to gain deep access to a car’s network. It demonstrates implanting a persistent backdoor, establishing a reverse shell, and leveraging exposed ADB and other services…
Slide deck 2025
45 Mins
Offensive Security Engineering Why your TARA needs a reality check
- Jannis Kelter Head of Cybersecurity, Holon
The Threat Analysis and Risk Assessment (TARA) is a central element of the cybersecurity engineering process in the automotive domain, as mandated by ISO/SAE 21434. It defines the rationale for security controls and documents system-level risks…
Slide deck 2025
39 Mins
Simulating and Evaluating Incident Response for Automotive Systems
- Sergej Weber Lead Consultant and Cybersecurity Instructor , Kugler Maag Cie by UL Solutions
- Felix Bru00e4unling Principal Software Engineer, UL Solutions - Software Intensive System
Required innovation in the automotive market is driven by inter-connectivity and software, increasing the attack surface. In the case of an actual incident, companies should be prepared to respond appropriately, and to ensure this in the…
Slide deck 2025
59 mins
PANEL DISCUSSION | State of the Industry
Dr. Joern Eichler, Head of Security Engineering, Volkswagen AG · Markus Tschersich, Head of Security & Privacy Research and Governance, AUMOVIO · Faye Francy, Executive Director, Auto-ISAC, inc. · Christoph Krauß, Professor for Network Security / Head of Automotive Security Research, Darmstadt University of Applied Sciences / INCYDE GmbH
As vehicles become increasingly connected, the cybersecurity landscape is evolving at a rapid pace. This timely discussion brings together leading voices from industry and academia to explore the challenges, innovations, and strategies shaping the future of…
 2025
58 Mins
KEYNOTE | Are We There Yet Charting the Course for Long Term Vehicle Security
- Robert Kaster Bosch Americas Chief Technical Expert, Bosch
Automotive security has come a long way but where are we really headed? In this session, Bosch Chief Technical Expert Robert Kaster takes us on a journey through the history of automotive security from an engineer’s…
Slide deck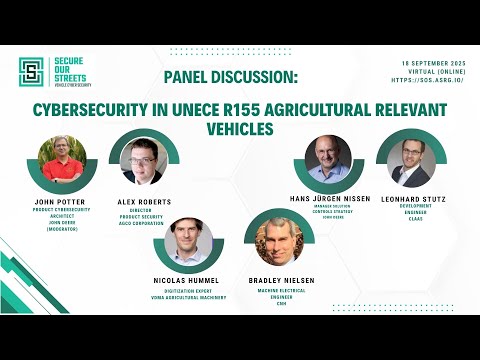 2025
1 hour
PANEL DISCUSSION | Cybersecurity in UNECE R155 Agricultural relevant Vehicles
- Nicolas Hummel Digitization Expert, VDMA Agricultural Machinery
- John Potter Product Cybersecurity Architect, John Deere
- Hans Juergen Nissen Manager Solution Controls Strategy , John Deere
- Alex Roberts Director, Product Security, AGCO Corporation
- Leonhard Stutz Development Engineer, CLAAS
As agricultural machinery becomes increasingly connected and automated, cybersecurity has emerged as a critical factor for safety, compliance, and operational resilience. This panel discussion at SOS 2025 will explore the potential implications of the UNECE R155…
 2025
45 Mins
Implementing Continuous Threat Exposure Management CTEM
Chris Mandich, Director of Cybersecurity Operations, Rivian · Juso Ahmetspahic, Detection and Response Team Lead, Rivian · Rob Hartman, Senior Staff Cybersecurity Engineer, Rivian
The rapidly evolving threat landscape targeting the automotive sector, particularly with the rise of Software-Defined Vehicles (SDVs) and extensive connectivity across vehicle, cloud, and charging ecosystems, necessitates a shift from traditional, static security testing towards dynamic,…
Slide deck 2025
41 Mins
The Cyber Resilience Act and its Implications on the Automotive Industry
- Stefan Rocksch Senior Manager , Deloitte Cyber Team
The regulatory landscape for automotive cybersecurity is undergoing significant transformation. On one hand, emerging domain-specific standards such as ISO/SAE PAS 8477 and ISO/SAE TR 8475 are contributing to the harmonization of automotive specific cybersecurity concepts. On…
Slide deck 2025
36 Mins
Blind Wireless Seed Key Exchange
Anne Zachos, Cybersecurity Research Engineer, NMFTA
Anne Zachos is a Cybersecurity Research Engineer at the National Motor Freight Traffic Association, Inc. (NMFTA)™. Anne has a strong background in embedded systems engineering and is dedicated to advancing cybersecurity within the trucking industry. Her…
Slide deck 2025
46 Mins
SBOMs in the Automotive Industry Real World Insights and Recommendations
- Cortez Frazier Jr Principal Product Manager, FOSSA
A heightened global focus on software supply chain security — plus a range of emerging industry regulations — have made SBOMs (software bill of materials) an increasingly important initiative for automotive suppliers and manufacturers. Of course,…
Slide deck 2025
41 Mins
Exploit Story | AutoRFKiller The Tool That Unlocked Thousands of Cars and Earned Me Two CVEs
- Danilo Erazo Independent Automotive Security Researcher
This session presents the development and impact of AutoRFKiller, a tool designed to exploit vulnerabilities in cars using learning code RF (radio frequency) technology for remote locking and unlocking. Over more than a year, the discovery…
Slide deck 2025
17 Mins
 2024
 2024
30 mins
Welcome!
John Heldreth
 2024
 2024
1 hr
KEYNOTE Raising the Cybersecurity bar Seeking unconventional methods to solve conventional problems
- Dr. Ahmad MK Nasser Senior Manager | Lead Security Architect and Team Manager of DRIVE OS, NVIDIA United States
KEYNOTE PRESENTATION: In the rapidly evolving automotive cybersecurity landscape, engineering teams face increasing security challenges, particularly with software-defined vehicles. Securing these complex, interconnected automotive systems is becoming more difficult as adversaries enhance their capabilities. This talk…
Slide deck 2024
1 hr
PANEL DISCUSSION Automotive Privacy – Differentiator or Pain in the Neck
Misha Rykov, Independent Investigative Researcher Germany · Mario Hoffman, Group Lead Cyber Security, ARRK Engineering GmbH Germany · Andrea Amico, Founder & CEO, Privacy4Cars United States · PD Dr. Sebastian Pape, Security & Privacy Manager, Continental Automotive Technologies GmbH Germany
Let’s assume that privacy (the right to be left alone) is a fundamental human right. As we know, there is data protection regulations worldwide which are supposed to be reflected, specifically, in business models and application…
 2024
45 mins
TAF as Steel A practical example for applying Targeted Attack Feasibility in an ECU Project
- Janos Kovacs Cyber Risk Analyst, Cymotive Budapest, Hungary
This presentation aims to provide an explanation and practical interpretation on the topic of Targeted Attack Feasibility (TAF, specified by ISO/SAE AWI PAS 8475). TAF is a concept that serves as a harmonized approach for managing…
Slide deck 2024
45 mins
Tales from a Penetration Testing Team Insights on Recent Zero Day Automotive Vulnerabilities
- Amit Geynis Security Research Team Leader, PlaxidityX Israel
We're all familiar with the term "Zero-Day Vulnerabilities" but have you ever wondered what kinds are found in real-time embedded automotive systems today? Our penetration testing team reverse-engineers many ECUs from clients, uncovering zero-day vulnerabilities in…
Slide deck 2024
30 mins
EVSE Security and the need for collaboration
- Adam Laurie Chief Product Security Officer, ALPITRONIC GMBH Bolzano, Italy
Explore the unique cybersecurity challenges faced by Electric Vehicle Supply Equipment (EVSE) and why traditional approaches fall short. This session will highlight the necessity for a collaborative strategy to address evolving threats and enhance the security…
 2024
45 mins
Exploiting EV Charging Networks Pathways to Potential Blackouts
- Lionel R. Saposnik VP of Security Research, SaiFlow
This talk explores the recent vulnerabilities in EV charging networks, focusing on how threat actors could exploit these weaknesses to cause large-scale blackouts. By examining critical issues in EV chargers, Charging Station Management Systems (CSMS), and…
Slide deck 2024
45 mins
Securing the Keys to the Future Robust Authentication for Next Gen Vehicles
- Carlo Bauer Student, HS Mannnheim Germany
- Fabian Maas Student, HS Mannnheim Germany
- Gesa Mu00fcller Student, UAS Mannheim Germany
- Orell Schwarzbach Student, UAS Mannheim Germany
This presentation addresses solutions for mitigating critical vulnerabilities in automotive keyless entry systems. Our approach combines challenge-response authentication with timestamp verification to prevent relay and replay attacks that enable vehicle theft. We introduce the theoretical foundations…
Slide deck 2024
45 mins
From Regulation to Practice Frameworks for Cybersecurity Manager to Enable Better Cybersecurity
Manuel Sandler, Independent Automotive Consultant Germany
Why a systematic empowerment of the Cybersecurity Manager is more beneficial than just randomly targeting personal and company certifications. Real-world approaches that combine cybersecurity with leadership principles, people management, education, and processes.
Slide deck 2024
45 mins
Shifting Left Vulnerability Management
- Andreas Weichslgartner Senior Technical Security Engineer, CARIAD SE Germany
- Vineeth B. Prasanna Senior Technical Security Engineer, CARIAD SE Germany
As the automotive industry undergoes a paradigm shift towards software-defined vehicles, the imperative for robust software security becomes obvious. This talk explores the nuanced landscape of identifying, managing, and preventing vulnerabilities early in the product lifecycle…
Slide deck 2024
45 mins
Redefining OEM Supplier Dynamics Powerful TARA Updates for Effective Requirements Specifications
Falk Mayer, Co-Founder & Managing Director, BreachLabz Munich, Germany
Understanding and mitigating weak links in the automotive supply chain is crucial for comprehensive vehicle cybersecurity. This presentation explores the necessity of Threat Analysis and Risk Assessment (TARA) at all supply chain levels and offers practical…
Slide deck 2024
45 mins
Risk assessment along the supply chain From OEM to Tier 1 to Tier 2 – how does it all fit together
- Thomas Liedtke Senior Cyber Security Manager , Magility Cyber Security GmbH Germany
In a typical situation, a supplier (Tier-1, Tier-2, …) is asked to perform “own” TARAs on their level. In the end, the results have to be consistent with the vehicle TARA. Cybersecurity requirements coming from customers…
Slide deck 2024
30 mins
Driving Efficiency: Validating Your Security Posture With Sector Relevant Intelligence
- Jermain Njemanze EMEA Lead Solution Engineer, Filigran France
As connected and autonomous vehicles advance, the automotive industry faces increasingly complex cyber threats. This presentation highlights today’s most common threats and explores how to effectively integrate Cyber Threat Intelligence (CTI) into security operations. Our live…
Slide deck 2024
45 mins
An Investigation into Retrievable PII Data from a Mercedes Benz NTG6 IVI Module
Richard Harding, Digital Forensics Student, University of South Wales United Kingdom
This presentation explores the technique employed to perform a forensic acquisition of a publicly obtained Mercedes-Benz NTG6 infotainment module, the methods used to analyse data, revealing Personally Identifiable Information (PII) such as connected devices, phonebook records,…
Slide deck 2024
45 mins
The Complex Regulatory Landscape of Automotive Cybersecurity Challenges of National Standards
- Janine Funke Lead Strategic Area Cybersecurity, UL Solutions, Software Intensive Systems Germany
 2024
45 mins
Practical Transformation Proposal between CVSS 4 0 and ISO SAE 21434 Attack Feasibility Rating
- Oliver Huppenbauer Global Cybersecurity Manager, Marquardt GmbH Germany
- Orhun Su00fczer Independent Consultant, Orhun Su00fczer | Masters in Embedded Systems Stuttgart, Germany
Following our previous paper presented at the 2023 Secure our Streets (SoS), titled "A Practical Transformation Proposal between Attack Potential-based and CVSS-based Attack Feasibility Ratings," we received significant positive feedback and numerous requests for an update…
Slide deck 2024
30 mins
Everything Everywhere All at Once Towards Integrated Product Security for Software Defined Vehicle
- Jonathan Mohring President, itemis Inc. United States
- Dirk Leopold Executive Vice President, Digital Engineering, Itemis AG Germany
In today's world, software-defined vehicles require continuous development even after production. Releasing feature and security enhancements via OTA updates is the new normal for many automotive OEMs. However, doing this efficiently while managing complexity and risk…
Slide deck 2024
45 mins
The Missing Link How we collect and leverage SBOMs
- Cassie Crossley VP, Supply Chain Security, Cybersecurity & Product Security Office, Schneider Electric United States
There is some debate as to how SBOMs can enhance vulnerability management practices, and some believe that collecting SBOMs from internal teams or suppliers is too difficult and time-consuming. Learn how Schneider Electric has collected thousands…
Slide deck 2024
 2024
30 mins
CRISKLE An Integrated Product Security Lifecycle Platform for Enhanced Safety & Security Analysis
- Saket Mohan Founder and CEO, Secure Elements
In an era where mobility systems are rapidly evolving with advancements in technology, the integration of safety and security has become paramount. This presentation will delve into the critical need for a cohesive approach to safety…
Slide deck 2024
45 mins
Enhancing Automotive Cybersecurity Using Machine Learning techniques to Improve ISO SAE 21434
Atefeh Asayesh, Vehicle Cybersecurity Analyst, Block Harbor Cybersecurity United States · Minha Mir, Vehicle Cybersecurity Manager, Block Harbor Cybersecurity United States
This presentation explores how machine learning (ML) techniques can transform ISO/SAE 21434’s reactive framework into a dynamic, proactive one. By leveraging ML algorithms for anomaly detection, predictive risk assessment, and automated threat detection, the framework can…
Slide deck 2024
45 mins
Secure Isolation
- Ionut Racaru Senior Expert, Elektrobit Romania
- Gabriel Byman Senior Cybersecurity Product Manager, Elektrobit Automotive Oulu, Finland
- Elisabeth Waitz Senior Expert Cybersecurity, Elektrobit Germany
This presentation elaborates on secure isolation as a substantial element of a secure architecture. It especially focuses on the realization of isolation in software using operating systems and hypervisors and the challenges of providing HSM services…
Slide deck 2024
 2024
45 mins
Automotive Bug Bounty Program and Lessons Learned
- Karl Schlauch Principal CyberSecurity, VicOne Germany
During the inaugural Pwn2Own Automotive 49 unique zero-day vulnerabilities were discovered, affecting various connected car systems and components - including infotainment dashboards, operating systems, and electric vehicle (EV) chargers. We are discussing most common entry points,…
Slide deck 2024
 2024
 2024
15 mins
Closing
John Heldreth
 2023
 2023
Welcome!
John Heldreth
 2023
 2023
 2023
 2023
 2023
 2023
 2023
 2023
Kamel Ghali
Falling Backwards Into Automotive Security
 2023
 2023
 2023
 2023
 2023
 2023
 2023
1 hour
PANEL DISCUSSION Maturity of Cybersecurity Management Systems in Automotive Insights from Auditors
- Jako Fritz
- Dirk Ruberg
- Thomas Thurner
- Johana Constante Pu00e9rez
- Dr. Jetzabel M. Serna-Olvera
In this panel, we will explore the maturity for CSMS implementations across the automotive industry, and how it varies in different markets. We will discuss the most common process gaps and key challenges that OEMs and…
 2023
 2023
 2023
 2023
 2023
 2023
 2023
 2023
 2023
Closing
John Heldreth
 2022
45 mins
Welcome!
Conference opening.
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
 2022
Session 9
Rump Session
 2022
 2022
 2022
 2022
 2022
 2022
No talks match your filters.